
Cybersecurity Readiness: Your Roadmap for 2026
 October 16th, 2025 | 11:00 AM ET
Measuring Today. Prioritizing Tomorrow.
True resilience begins with readiness and readiness extends far beyond compliance. It represents a measurable state of preparedness across people, processes, and technology, enabling organizations to withstand and respond effectively to real-world threats. Boards and regulators now demand a defensible baseline of cyber maturity, supported by concrete evidence rather than assumptions.
This webinar presents a structured methodology for assessing current readiness and transforming those insights into a strategic roadmap for 2026 priorities.
Our Speakers
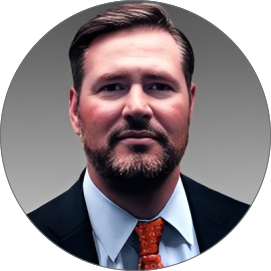
Paul Kelley
CEO
DCube Data Sciences Corporation 
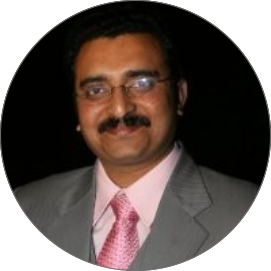
Dwarkanath Sundar
Co-Founder & Director
DCube Data Sciences Corporation
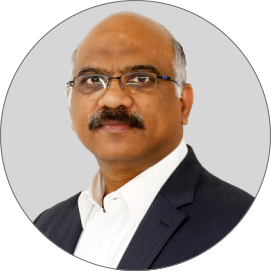
Anil Kona
Executive Director, COO
Covasant Technologies
Key Discussion Areas

Regulatory Benchmarks
Understanding where your organization stands today against FFIEC guidelines and the NIST Cybersecurity Framework and anticipating where standards are evolving.

Testing Readiness
Leveraging penetration testing, dark web monitoring, and maturity diagnostics to validate actual security posture rather than perceived capabilities.

Controls and Assessments
Employing structured assessment instruments, including comprehensive 600-question readiness reviews, to identify systemic vulnerabilities and gaps.

The Readiness Triad
Exploring why organizational resilience requires balanced investment across people, processes, and technology, and the interdependencies between these pillars.
Testing Readiness
Converting assessment findings into actionable, prioritized improvement strategies that drive meaningful progress in 2026.